This is default featured post 1 title

Go to Blogger edit html and find these sentences.Now replace these sentences with your own descriptions.

This is default featured post 2 title

Go to Blogger edit html and find these sentences.Now replace these sentences with your own descriptions.

This is default featured post 3 title

Go to Blogger edit html and find these sentences.Now replace these sentences with your own descriptions.

This is default featured post 4 title

Go to Blogger edit html and find these sentences.Now replace these sentences with your own descriptions.

This is default featured post 5 title

Go to Blogger edit html and find these sentences.Now replace these sentences with your own descriptions.

Showing posts with label PasswordCracking. Show all posts

Sunday, 1 April 2012

GUI For The John The Ripper -JOHNNY Is Launched.


 Johnny is a GUI for John the Ripper. It was proposed by Shinnok. s release includes all things from development release plus nice tabbed panel for mode selection and some additional clean-ups. Basic functionality is supposed to work: password could be loaded from file and cracked with different options.


The reasoning behind Johnny is simple but at the same time profound: Complexity through simplicity and non-intrusive expert and non-expert availability. Johnny is a GUI concept to John the Ripper written in C++ using the Qt framework, making it cross-platform on both Unix/Linux and Windows operating systems.
                                             

It was programmed as a part of the Google Summer of Code 2012 and supports bother 32-bit and 64-bit architectures. The interface also leaves room for lots of new options, either future John options, as well as GUI specific options like, hash detection, dictionary editing and generation or interactive bruteforce charsets or rules creation and many more.
Download Jonny

Tuesday, 14 February 2012

THC-Hydra v7.2 released :A very fast network logon cracker .

Hydra is a parallized login cracker which supports numerous protocols to attack. New modules are easy to add, beside that, it is flexible and very fast. Hydra was tested to compile on Linux, Windows/Cygwin, Solaris 11, FreeBSD 8.1 and OSX, and is made available under GPLv3 with a special OpenSSL license expansion.


CHANGELOG for 7.2
=================
* Speed-up http modules auth mechanism detection
* Fixed -C colonfile mode when empty login/passwords were used (thanks to will(at)configitnow(dot)com for reporting)
* The -f switch was not working for postgres, afp, socks5,
* firebird and ncp, thanks to Richard Whitcroft for reporting!
* Fixed NTLM auth in http-proxy/http-proxy-url module
* Fixed URL when being redirected in http-form module, thanks to gash(at)chaostreff(dot)at
* Fix MSSQL success login condition, thanks to whistle_master(at)live(dot)com
* Fix http form module: optional headers and 3xx status redirect, thx to Gash
* Fix in configure script for --prefix option, thanks to dazzlepod
* Update of the dpl4hydra script by Roland Kessler, thanks!
* Small fix for hydra man page, thanks to brad(at)comstyle(dot)com

Download it from here:
http://www.thc.org/thc-hydra/

Monday, 6 February 2012

How to hack IIS ( internet information server ) FTP password by useing Brute Force Attack.

FTP is an application or service or protocol which can be used to transfer files from one place to another place ,it really comes very handy during transfer of files from a local box to a remote one .Suppose someone get access to your FTP then he/she can cause nightmare for you by uploading unappropriate images or files etc.Here we will discuss how we can crack the password of IIS installed FTP service in Windows.


What is Brute-Force?

Brute-force is a type of attack in which every possible combination of letters, digits and special characters are tried until the right password is matched with the username. The main limitation of this attack is its time factor. The time it takes to find the proper match mainly depends on the length and complexity of the password.Here I will be using this attack to crack the password.So,lets start….
Requirements:
  1. The tool we will be using ” BrutusA2”(Download: http://www.hoobie.net/brutus/)
  2. You need to know the target suppose “ftp://123.123.xx.xxx”

Procedure:

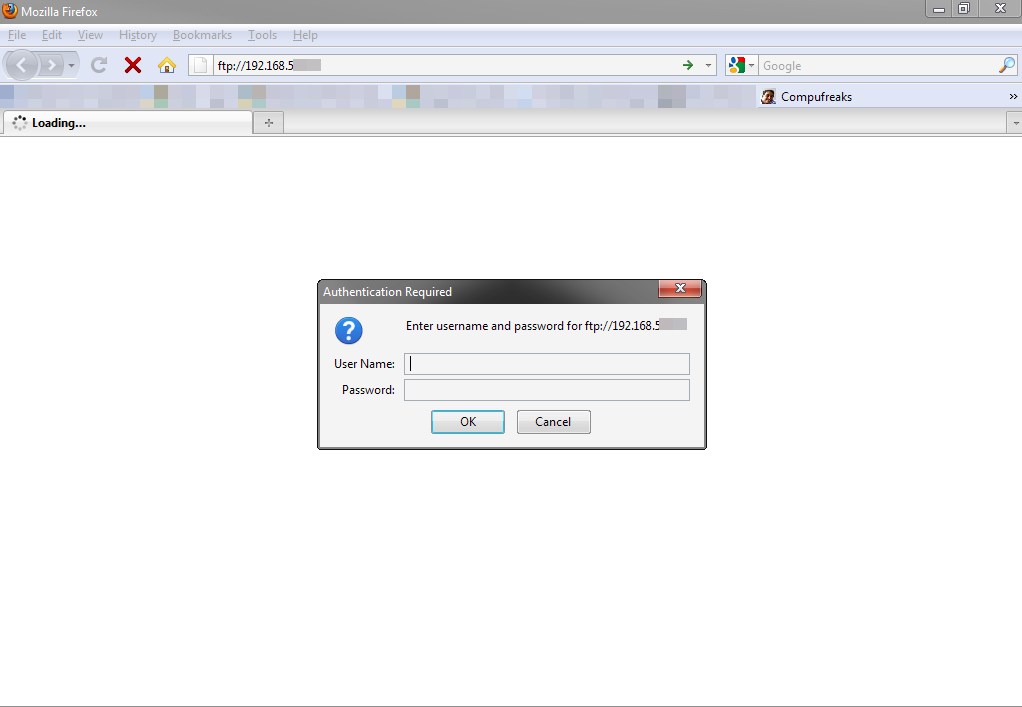
Step 1.Here I have shown an authentication page of an FTP service in the image below and in the following steps we will crack its password using brutus.

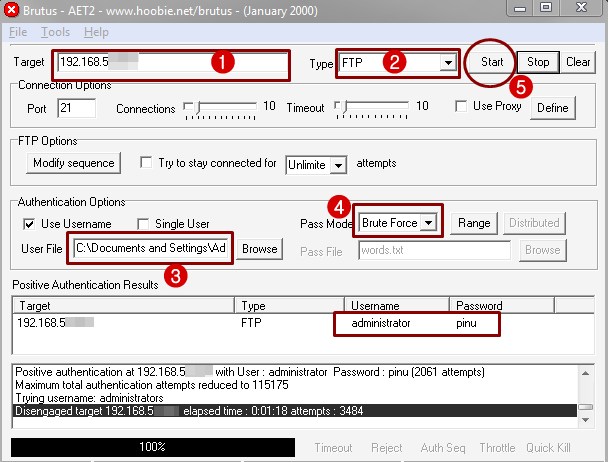
Step 2.Now open up “Brutus” and type your desire target ,select wordlist and select “FTP” from the drop down menu and click start. If you are confused then follow the image below.


Step 3.The time it takes as I mentioned above depends on the complexity and length of the password.So after clicking the start button wait for the time as mentioned in the tool.The password will be displayed as shown above.
Recommendation: I would recommend the readers to try it in a virtual environment as I did and enjoy the trick.It is not advisable to try it on some unknown user without prior permission.